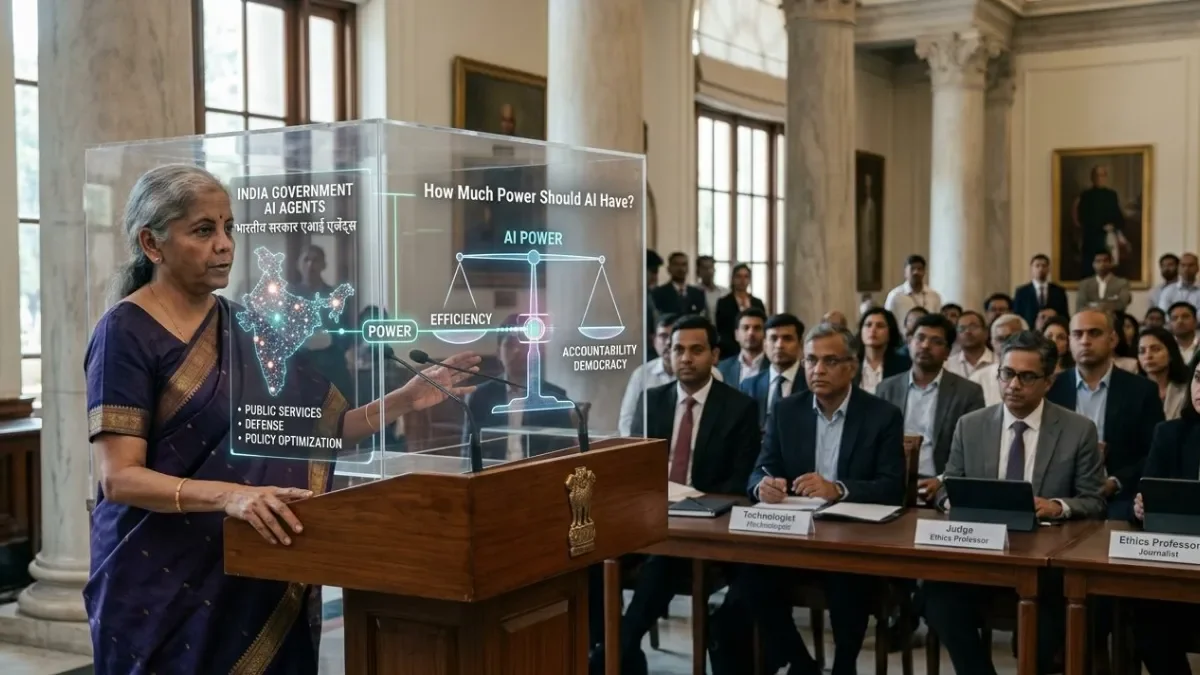
India is moving artificial intelligence deeper into government operations, and the next phase is not just about chatbots answering questions. Government bodies are exploring AI systems that can work with documents, interact with approved tools, support procurement, modernise legacy software and assist cybersecurity teams.
That shift creates a much bigger question than whether AI is useful: how much authority should an AI system be allowed to exercise when it is working on behalf of the government?
How is India using AI inside government?
India's government AI push is increasingly connected to the country's wider digital public infrastructure.
The National e-Governance Division (NeGD) under MeitY has proposed a reusable AI assistant platform with an LLM-driven, agentic architecture. DigiLocker is being considered as a reference implementation, with the broader idea of creating components that can eventually be reused across government services.
This is different from a conventional chatbot.
A chatbot generally responds to a question. An AI agent can potentially understand an objective, plan several steps, access authorised tools and carry out parts of a workflow.
That could eventually mean a citizen asking an AI system for help with a government service and having the system retrieve information, identify the required documents and guide or complete parts of the process.
The potential benefit is obvious in a country where government services can involve multiple departments, databases and forms.
But the moment AI moves from giving information to taking action, the risk calculation changes.
Why is DigiLocker an important example?
DigiLocker already sits within India's digital public infrastructure and is designed to give citizens access to digital documents and certificates.
The proposed AI assistant could use DigiLocker as an early implementation environment. The larger objective is reportedly to create reusable components such as consent management, analytics and AI services rather than developing an isolated chatbot for one department.
That approach could make government AI more scalable.
It could also make mistakes more consequential.
If an AI merely gives an incorrect answer about where to download a certificate, a human can usually correct it. If an agent retrieves the wrong record, sends incorrect information, submits something to another government system or performs an action without adequate authorisation, the consequences can be much harder to reverse.
This is why permission boundaries matter as much as model accuracy.
Is the government also using AI for procurement?
Yes. Government procurement is another area where AI is being introduced.
An AI-powered platform is being developed to assist government departments with procurement-related documents, including material such as requests for proposals, requests for quotations and expressions of interest.
This could reduce the amount of repetitive drafting and document preparation officials have to perform.
But procurement is not simply a writing exercise. Government tenders can determine how public money is spent and which companies get opportunities to supply goods or services.
An AI system therefore needs to be treated as an assistant with controlled authority, rather than an autonomous decision-maker.
The distinction is important: helping prepare a document is very different from deciding which supplier should win a contract.
What role could AI play in government cyber defence?
Cybersecurity may be one of the areas where giving AI greater operational capability makes the most sense.
CERT-In, India's national agency for responding to cybersecurity incidents, has been experimenting with AI models to understand how they could help identify and remediate vulnerabilities at scale. The agency has also been conducting dry runs involving advanced AI models.
AI can potentially analyse huge volumes of security information much faster than human teams.
That matters because cyberattacks can happen at machine speed. A system capable of continuously examining vulnerabilities, suspicious activity and possible attack paths could give defenders an important advantage.
But the same technology can also strengthen attackers.
The result is a new cybersecurity environment in which AI may be operating on both sides of the fight. Recent cybersecurity discussions have highlighted the possibility of AI agents becoming targets themselves, creating new problems around identity, permissions and attribution.
For government systems, that makes access control particularly important.
Why are legacy government systems part of the AI conversation?
A large amount of government technology was built before today's AI systems existed.
India's National Data Governance framework explicitly addresses interoperability, standardisation and the use of data wrappers for legacy systems. It also identifies platforms including API Setu, NAPIX, AIKosh, IUDX, DigiLocker and Entity Locker as part of the broader data-exchange architecture.
AI agents could eventually act as a new layer over some of these older systems.
That could be useful because replacing every legacy system at once would be expensive and disruptive. An AI layer could potentially help translate natural-language requests into structured actions across existing software.
But connecting AI to old systems also creates another security concern: every additional connection can become another route into sensitive infrastructure.
What happens when an AI government agent makes a mistake?
This may be the hardest question of all.
Suppose an AI agent misunderstands a citizen's request and submits incorrect information. Or it interprets an eligibility rule incorrectly. Or it accesses the wrong government record.
Who is responsible?
The AI itself cannot be held accountable in the same way as a government official, department or contractor. The responsibility therefore has to remain with identifiable institutions and people.
Finance Minister Nirmala Sitharaman recently made a similar point while discussing agentic AI and emerging technology, stressing that responsibility for AI decisions should remain institutional and human, particularly for high-impact actions.
That principle becomes especially important when an AI system is connected to government databases or services.
Should AI be allowed to make government decisions?
Not every government task should have the same level of AI autonomy.
A useful way to think about it is to divide government AI actions into different risk levels:
| AI Role | Example | Suggested Human Control |
|---|---|---|
| Information | Answering a citizen's question | Low |
| Assistance | Finding documents or explaining a process | Moderate |
| Drafting | Preparing procurement documents | Human review |
| Recommendation | Suggesting eligibility or next steps | Strong human review |
| External action | Submitting applications or changing records | Explicit approval |
| High-impact decision | Affecting benefits, legal status or public funds | Human decision-maker |
The more an AI action can affect a person's rights, money, records or access to government services, the stronger the human oversight should be.
Why do AI agents need more than cybersecurity safeguards?
Cybersecurity is only one part of responsible government AI.
A system can be technically secure and still make a harmful decision.
For example, an AI could authenticate correctly, access the correct database and follow its instructions perfectly — but interpret a complicated rule incorrectly.
That means government AI needs safeguards covering accuracy, explainability, auditability, permissions, privacy and the ability to challenge an automated outcome.
The government's proposed AI assistant framework reportedly includes evaluation around areas such as hallucinations, tool accuracy, multilingual performance and safety, along with monitoring of agent behaviour.
Those measures are important because an AI system should not be judged only by how impressive its answers look.
What does India's data protection framework mean for government AI?
This question becomes particularly important when AI systems interact with large stores of personal information.
India's Digital Personal Data Protection framework is part of the broader regulatory environment around the processing of personal data. Meanwhile, government AI systems are being designed around platforms and datasets that can contain highly sensitive citizen information.
The challenge is therefore not simply preventing a data breach.
Government AI needs clear rules about what information an agent can access, why it needs that information, how long access lasts and whether every action can be traced later.
A national data-sharing framework approved in 2026 also emphasises consent mechanisms, de-identification, dataset classification and a security-conscious approach to government data sharing.
What could responsible government AI look like?
India does not necessarily have to choose between completely manual government services and fully autonomous AI.
A middle path could involve AI doing the repetitive work while humans retain control over consequential decisions.
For example:
- AI understands the citizen's request.
- AI identifies the relevant government service.
- AI retrieves information only from authorised systems.
- AI explains what it intends to do.
- A human approves high-impact or irreversible actions.
- Every important action is logged for auditing.
- Citizens have a way to challenge or correct an AI-assisted outcome.
This model would allow government to benefit from automation without treating AI as an unaccountable authority.
Is India ready for agentic AI in government?
India clearly has the digital infrastructure and policy ambition to experiment with agentic AI.
The Comptroller and Auditor General of India, for example, issued an expression of interest in 2026 for a sovereign AI and data platform with agentic AI applications, showing that the concept is moving beyond theoretical discussions and into government technology procurement.
The real test, however, will not be how many AI pilots the government launches.
It will be whether those systems can operate safely inside complicated administrative environments without creating new problems around privacy, cybersecurity, bias, transparency or accountability.
The most important question may therefore not be “Can AI do this?”
It may be “Should AI be allowed to do this without a human?”
Frequently Asked Questions
What is agentic AI in government?
Agentic AI refers to AI systems capable of planning and carrying out multiple steps using authorised tools, rather than simply generating an answer.
How is India using AI in government?
Current initiatives include AI assistants linked to digital government services, AI-supported procurement, legacy-system modernisation and cybersecurity experimentation.
Can AI make government decisions on its own?
AI can potentially support recommendations and workflows, but high-impact or irreversible government decisions require clear human responsibility and appropriate oversight.
What is the biggest risk of government AI?
There is no single risk. Cyberattacks, excessive permissions, privacy failures, incorrect decisions and unclear accountability can all become serious problems as AI receives greater access to government systems.